Sounds like a you problem I've had multiple FreeBSD systems on vultr for over a decade and never had sshd issues. Of course I also use an alternate port and active fail2ban to block those who insist on any brute force for any protocol. 128K active blocks currently.
I met Ajit shortly after he started in his role. I specifically told him how we can track and trace back these robocalls via SS7 (at least once they hit the PSTN - SIP ingress even easier to track back to the trunks they originate), and I even had proof of concept code and examples. He seemed really excited, then did nothing. No follow-up, etc. It would only work if mandated by the FCC because there is no financial incentive for the telcos to do it.
I think the pressure to implement better ROA checking and something like RPKI will be much stronger than the push to IPv6 was if we keep having major route leaks multiple times a year.
Eventually some governments will have to get involved...


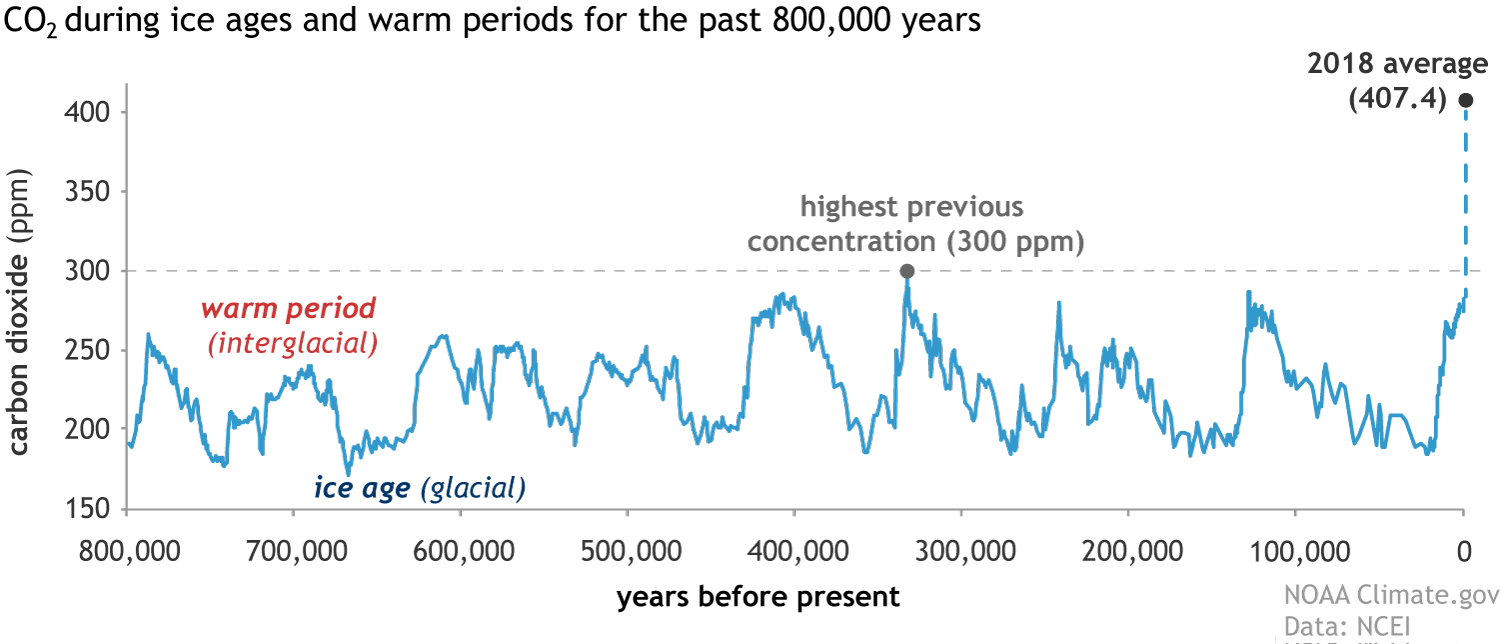
"At the moment we are speculating".. nothing more to see here.
reply